Docker bind mount permission denied
Docker bind mount permission denied? Verify the host path, container user and mount type before loosening permissions or rebuilding the image. This source-reviewed guide keeps the next action tied to the evidence you can collect safely.
Capture the exact symptom and scope first
Docker bind mount permission denied? Verify the host path, container user and mount type before loosening permissions or rebuilding the image.
- Record the exact visible error and timestamp.
- Check whether one target or several are affected.
- Preserve the relevant log, response or configuration state.
- Choose the next action only after identifying the affected layer.
Why this branch first: The exact message, timestamp and scope identify the next diagnostic layer more safely than broad resets or deletes.
Choose a local-first diagnostic tool
Use a TroubleByte tool to inspect an error, DNS record or local system context before changing settings.
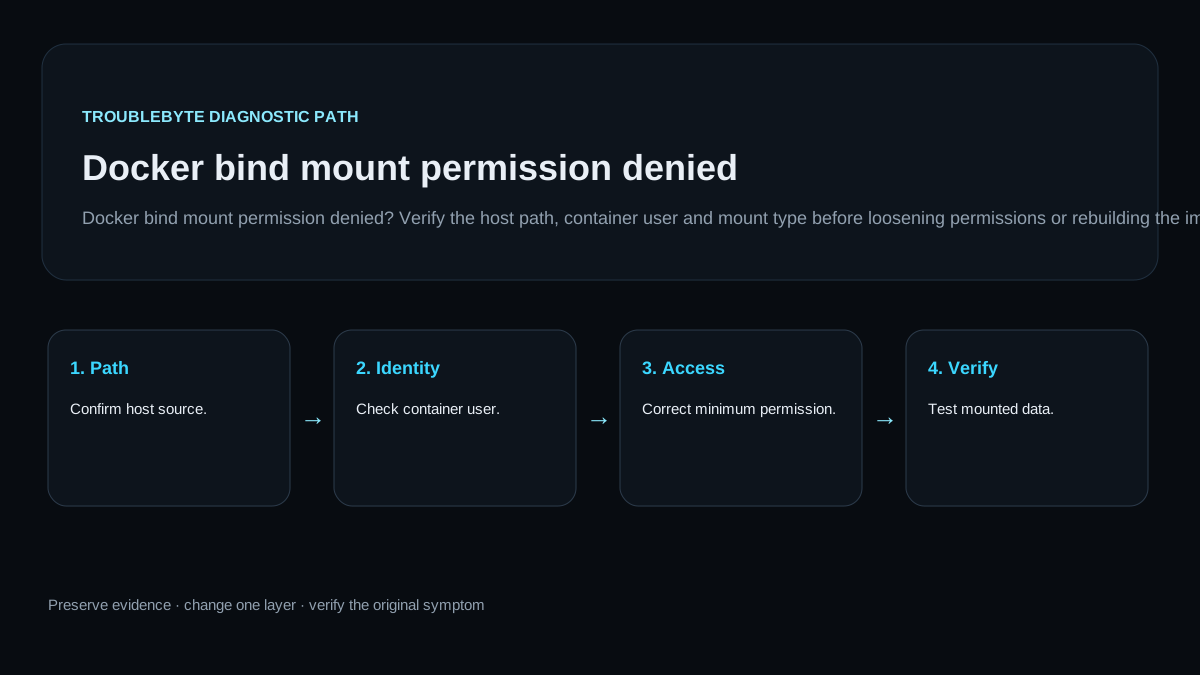
TroubleByte diagnostic path
Confirm host source.
Check container user.
Correct minimum permission.
Test mounted data.
Original TroubleByte diagnostic map. It summarizes the cited troubleshooting order; it is not a vendor screenshot.
Use the symptom to choose the next branch
Does the evidence point to one affected target rather than a wider platform, host or network failure?
Keep the correction narrow and verify it once.
Stop isolated changes and investigate the shared layer first.
Do you have the exact message, timestamp and relevant log or response evidence?
Follow the scoped diagnostic path.
Capture it before resets, deletes or broad configuration changes.
Original TroubleByte decision aid derived from the cited troubleshooting scope. It does not replace vendor documentation.
What this usually means
A bind mount exposes a host path into a container, so access depends on both the host path and the process identity used in the container. The failure may also be an unavailable shared folder on Docker Desktop. Avoid broad permission changes until the exact host path and container user are known.
What we verified from the source material
A bind mount exposes a host path into a container, so access depends on both the host path and the process identity used in the container. The failure may also be an unavailable shared folder on Docker Desktop. Avoid broad permission changes until the exact host path and container user are known.
Prerequisites and checks
Prepare first
- Do not recursively grant world-writable permissions to a host directory.
- Do not replace a bind mount with an unnamed volume without preserving required data.
- Avoid broad resets, deletes or configuration changes until the affected scope is confirmed.
Checks that prevent the wrong fix
- Record the source path, destination path and full error.
- Confirm the source exists on the Docker host.
- Identify the user or UID that writes inside the container.
Applies to
Solutions, in order
Capture the exact symptom and scope first
- Record the exact visible error and timestamp.
- Check whether one target or several are affected.
- Preserve the relevant log, response or configuration state.
- Choose the next action only after identifying the affected layer.
Why this can work: The exact message, timestamp and scope identify the next diagnostic layer more safely than broad resets or deletes.
Match the host path and container access model
- Confirm the bind source and destination paths.
- Check source-path ownership and container user expectations.
- Correct the minimum required host permission or Docker Desktop sharing setting.
- Restart once and verify access to the intended path.
Why this can work: Apply a narrow correction that follows the observed evidence, then verify the original symptom is gone.
How to know the fix actually worked
- Confirm the intended container user can read or write only the required path.
- Restart one container and verify the mounted application data.
Do not count a temporary disappearance of the symptom as a confirmed fix if the problem normally returns after a restart, reconnect or several minutes of use.
When not to keep changing things
- If the mount contains sensitive host data, stop before broad ownership or permission changes.
Escalation: Escalate with the exact message, timestamp, affected scope and the checks already completed.
Sources used for this record
Primary · checked Sep 26, 2026Docker — Troubleshoot topics for Docker DesktopOfficial documentation used to verify scoped troubleshooting guidance.Corroborating · checked Sep 26, 2026Docker — Bind mountsOfficial documentation used to verify scoped troubleshooting guidance.Discuss this exact problem
Share what happened on your system, ask a focused follow-up question, or add evidence that may help someone with the same symptom. Community posts are separate from TroubleByte editorial verification.
Start a discussion
Revision history
Show 1 recorded revision
2026-09-26 — Created from current official documentation with scoped decisions, explicit stop conditions and an original TroubleByte diagnostic diagram.